Sanctions Screening for Merchant Onboarding: The PSP Checklist That Survives File Reviews | MatchAudit Learn
Sanctions Screening for Merchant Onboarding: The PSP Checklist That Survives File Reviews
A practical, audit-ready sanctions screening workflow for PSPs, acquirers, and marketplaces—covering who to screen, when to screen, how to reduce false positives, and what evidence to store for bank partner and auditor reviews.
•5 min read
Merchant onboarding is a growth lever—until it becomes a liability.
For PSPs, acquirers, PayFacs, and marketplaces, the real test isn’t whether you ran screening. The test is whether you can prove that screening was:
Done on the right parties (entity + UBOs + directors)
Done at the right time (onboarding + changes + periodic re-screening)
Done with defensible outcomes (why a match was cleared or escalated)
Documented in a way that survives partner due diligence, audits, and file reviews
This guide provides a practical checklist you can implement immediately—optimized for small compliance teams that need structured screening evidence without bank-sized headcount.
Who this is for
This checklist is designed for:
PSPs and acquirers onboarding merchants at scale
Marketplaces onboarding cross-border sellers and vendors
Payout platforms / payroll / mass disbursements onboarding payees and beneficiaries
Crypto and fintechs building “audit-ready” KYB/KYC controls
If your compliance program is judged by external parties (banks, schemes, enterprise partners), you need more than a “green check.” You need evidence.
The core principle: “screening happened” is not evidence
Many teams “pass operationally” but fail in file reviews because:
Matches are cleared with vague notes (“not the same person”)
Inputs aren’t preserved (what was screened, exactly?)
You cannot reproduce a result (list versions, configuration, timestamps)
There is no audit trail (who decided, when, and based on what)
The outcome: onboarding delays, escalations, reputational risk, and costly remediation.
Your goal is to create an audit-ready decision pack for every onboarding file—automatically.
Step 1 — Screen the right parties (minimum scope)
For each merchant relationship, screen:
A) The merchant entity (KYB scope)
Legal entity name (as registered)
Trade names / brand names
Local-language or transliterated variants (where relevant)
Registration country and key operating countries
B) Ownership and control persons (KYC/KYB overlap)
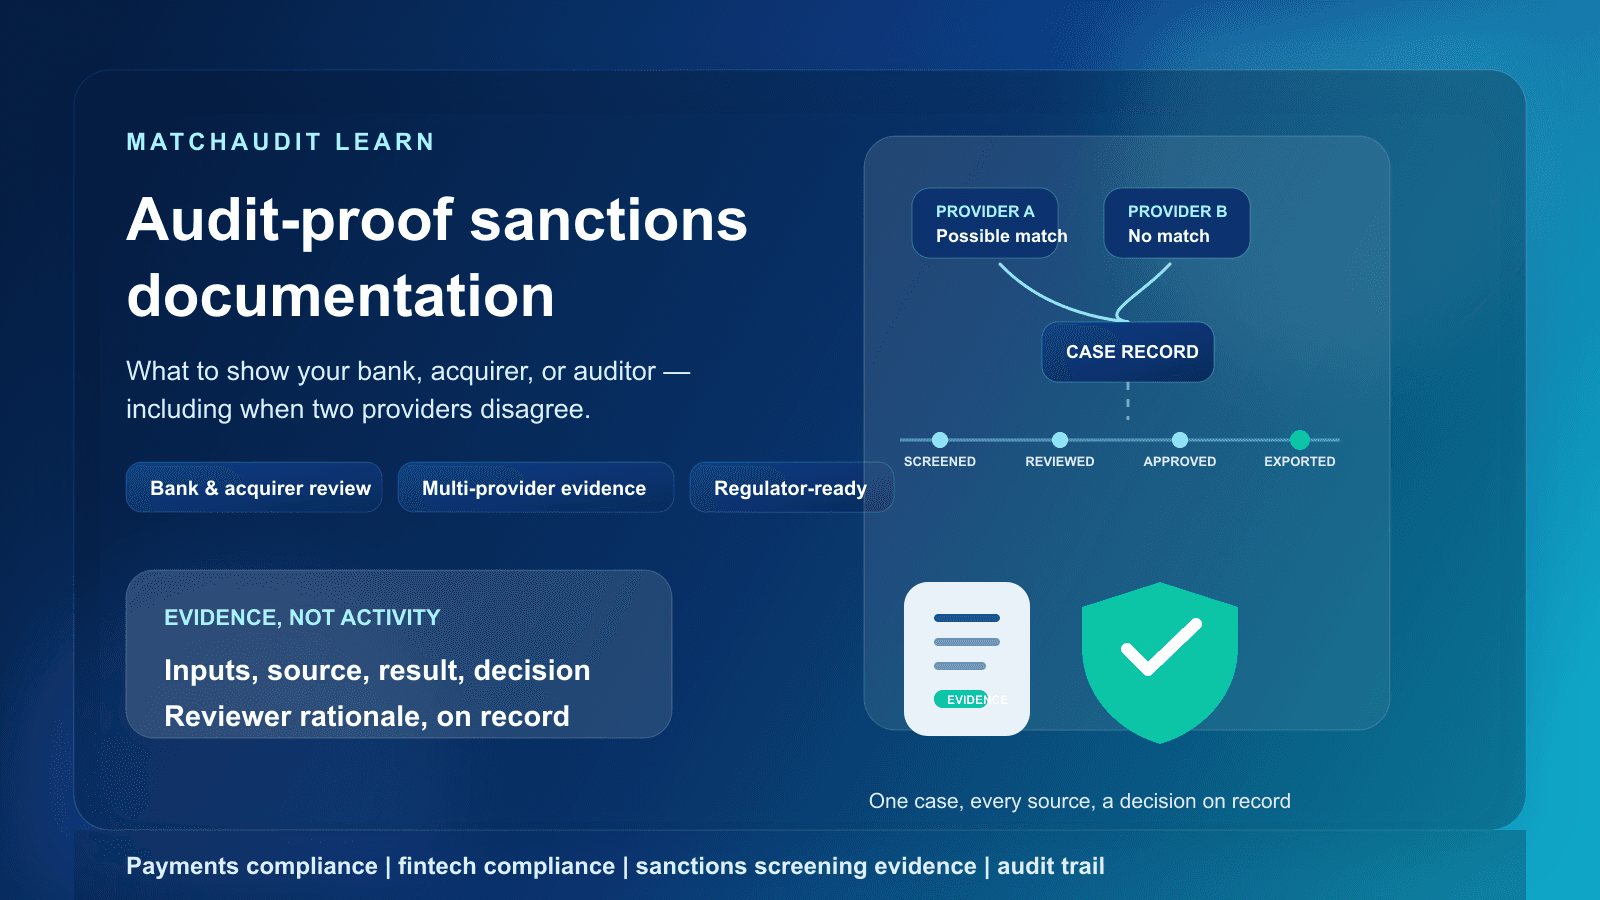
Store evidence: input, dataset versions, output, decision, audit trail
Produce PDF/CSV evidence pack on demand
Why MatchAudit is built for this exact problem
Most tools can “return a hit.”
MatchAudit is designed to produce structured evidence:
explainable matches (field-level)
normalized confidence scoring
structured decision trails
exportable reports for file reviews and partner due diligence
Call to action
If you want to validate this workflow quickly:
Start free: run a merchant + UBO screening and see audit-ready outputs
Request a pilot: we’ll set up directory re-screening + evidence pack exports aligned to your policy
See a sample evidence pack: use it internally to get buy-in from compliance leadership
Sanctions screening playbook for PSPs, freight forwarders and cross-border SMEs
A practical, risk-based sanctions screening blueprint for non-bank institutions like PSPs, freight forwarders, marketplaces and NGOs that need structured screening records without a bank-sized team.