18 Sept 2026
Bank Vendor Onboarding: Why Signed Contracts Get Stuck in Third-Party Risk Review
A practical guide to bank vendor onboarding, third-party risk approval, security questionnaires, due diligence evidence, and faster activation after the contract is signed.
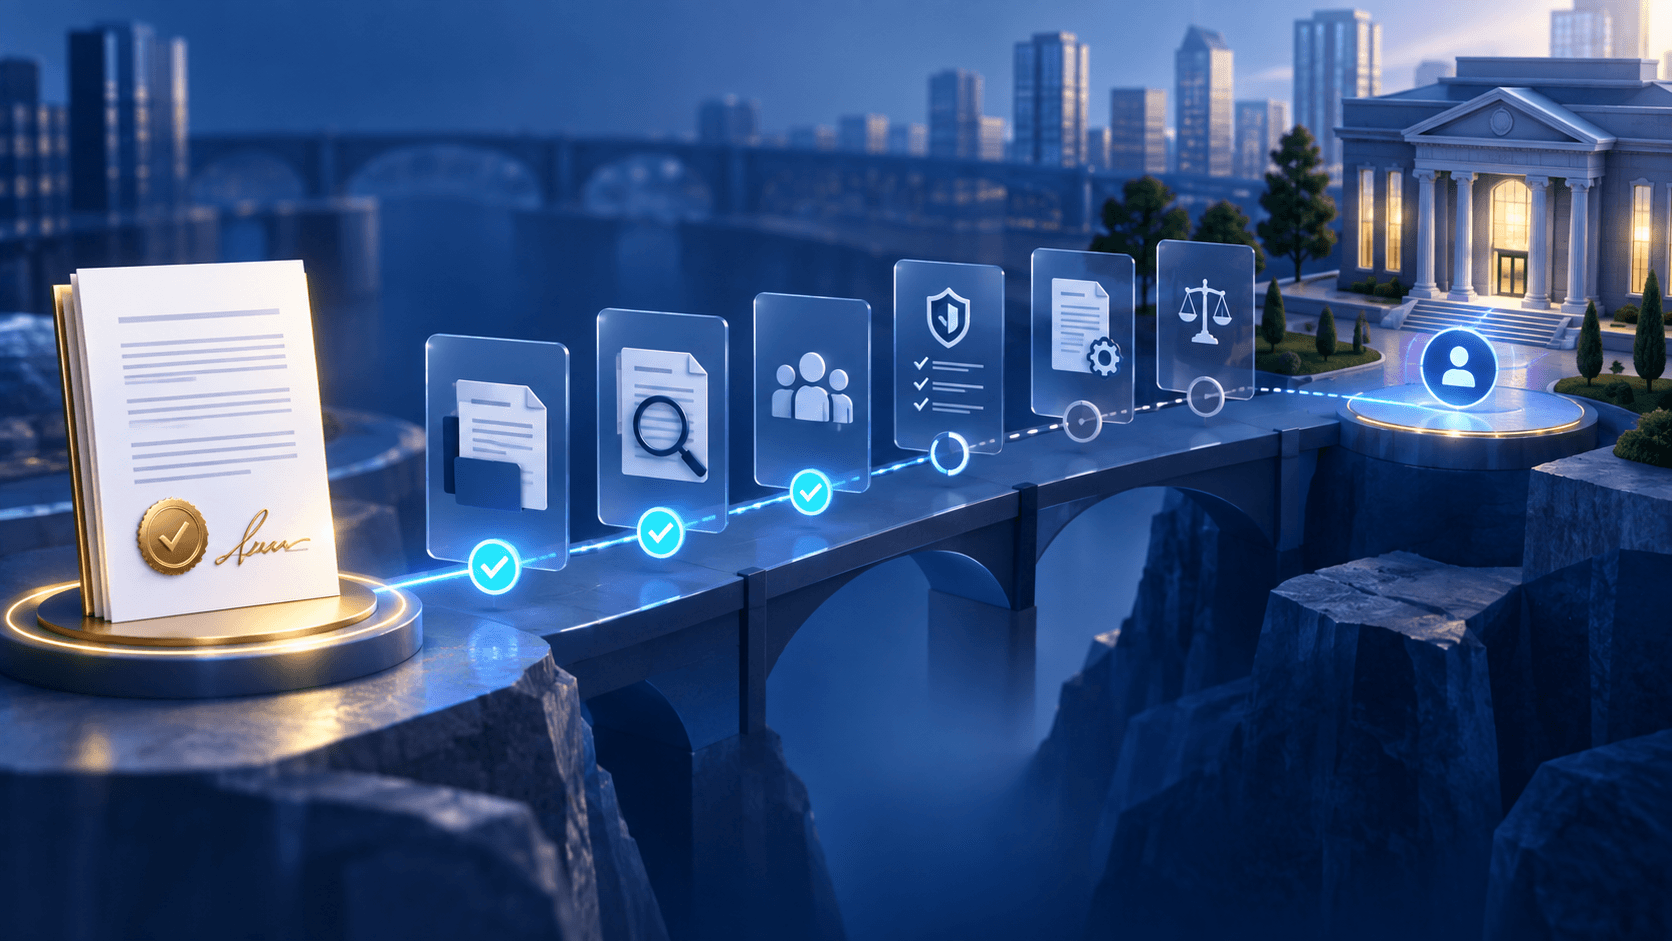
You won the bank.
The contract is signed. The commercial team celebrates.
But the customer is still not active - and the revenue is still waiting.
Why? Because the commercial decision and the bank's third-party risk approval are two different milestones.
For vendors selling software or services to regulated financial institutions, signing the contract may only start the operational part of the sale. Before activation, the bank may need to assess information security, data privacy, business continuity, financial stability, subcontractors, regulatory exposure, and the controls surrounding the service.
This guide explains why bank vendor onboarding becomes stuck, what a bank's third-party risk management (TPRM) process usually asks vendors to provide, and how vendors can build a repeatable process that moves a signed deal toward approval and activation.
Quick answer: A signed contract can remain inactive because procurement and third-party risk approval are separate processes. The fastest vendors do not treat each questionnaire as a one-off document exercise. They maintain reusable, owned, current evidence; translate each bank request into clear actions; track gaps and dependencies centrally; and keep a human accountable for every final response.
What is bank vendor onboarding?
Bank vendor onboarding is the process a financial institution uses to approve, set up, and monitor a third-party supplier before and during the business relationship. It can include procurement, legal review, information security assessment, privacy review, compliance checks, operational-resilience assessment, financial due diligence, technical integration, and final business approval.
The depth of review normally depends on the risk introduced by the service. A vendor that hosts sensitive customer data, connects to production systems, or supports an important business service will generally face more scrutiny than a supplier with no data access or operational dependency.
This is not simply administrative caution. US banking agencies describe third-party risk management as a lifecycle covering planning, due diligence and selection, contract negotiation, ongoing monitoring, and termination. In Europe, the EBA's outsourcing framework and the EU Digital Operational Resilience Act (DORA) place particular attention on governance, ICT dependencies, contractual arrangements, monitoring, and resilience.
For a vendor, that creates an important commercial reality:
The sale is not complete when the bank signs. The sale produces revenue when the customer is approved, implemented, and active.
Why a signed bank contract can still be waiting for approval
Commercial selection answers one question: Does the bank want to buy this product or service?
Third-party risk review answers another: Can the bank use this vendor within its risk appetite and regulatory obligations?
Those decisions involve different people, evidence, and approval rights. A business sponsor may be ready to proceed while security, privacy, legal, compliance, procurement, or operational-resilience teams still have open questions.
Before activation, the vendor may still need to:
- Interpret the bank's requirements
- Complete security and risk questionnaires
- Collect information from multiple internal teams
- Submit policies, certifications and supporting documents
- Resolve missing, inconsistent or outdated information
- Respond to follow-up requests
- Track approvals, deadlines and recurring reviews
The problem is rarely a lack of willingness.
It is the absence of a clear, coordinated process on the vendor side.
Sales, security, legal, compliance and product teams often contribute separately. Documents sit in different systems. Requirements are interpreted manually. No one has a complete view of what is missing, which answer is authoritative, who owns the next action, or what must happen before the bank can approve the relationship.
That is how a commercially won deal can remain stuck for months before activation.
The bank vendor onboarding process: seven common stages
Every institution uses its own terminology, but most onboarding journeys contain the following stages.
| Stage | What the bank is trying to establish | What the vendor should prepare |
|---|---|---|
| 1. Intake and inherent-risk assessment | What service is being purchased, which data and systems are involved, and how critical is the dependency? | A precise service description, data-flow summary, hosting model, integration scope, locations, and subcontractor overview |
| 2. Vendor due diligence | Is the supplier financially, legally, operationally, and ethically suitable? | Corporate records, ownership information, insurance, financial information, compliance statements, and relevant policies |
| 3. Information-security review | Can the vendor protect the bank's data and systems? | Security questionnaire, architecture and data-flow diagrams, access-control model, vulnerability-management approach, incident process, and independent assurance reports |
| 4. Privacy and data review | What personal data is processed, where, why, for how long, and by whom? | Data-processing details, retention and deletion rules, data locations, subprocessors, transfer mechanisms, and a DPA position |
| 5. Resilience and continuity review | Can the service withstand disruption and recover within acceptable limits? | Business continuity and disaster recovery plans, recovery objectives, test evidence, backup approach, availability commitments, and incident communications |
| 6. Contract and risk acceptance | Are audit, security, notification, subcontracting, data, resilience, and exit expectations reflected in the agreement? | Named legal and control owners, an issues log, agreed remediation dates, and clear responses to exceptions |
| 7. Activation and ongoing monitoring | Are all conditions complete, and how will the relationship be reviewed after launch? | Final approval evidence, implementation dependencies, renewal dates, certificate expiry dates, material-change triggers, and review ownership |
The sequence is not always linear. A security answer may create a contractual issue. A new subprocessor may trigger a privacy review. A resilience finding may require a product or infrastructure change. Good vendor-side coordination makes those dependencies visible early.
What documents do banks ask vendors to provide?
There is no universal bank vendor due diligence checklist. Requirements vary by institution, jurisdiction, service, data exposure, integration model, and risk tier. However, a reusable evidence library commonly includes the following categories.
Corporate and commercial evidence
- Legal entity and registration details
- Ownership and group structure
- Key contacts and escalation paths
- Insurance certificates
- Financial information or evidence of financial stability
- Service description, pricing scope, and implementation plan
Information-security evidence
- Information-security policy
- Access-control and identity-management policy
- Secure development and change-management practices
- Vulnerability and patch-management policy
- Penetration-test summary or remediation evidence
- Incident-response plan and notification process
- SOC 2 report, ISO 27001 certificate, or other applicable independent assurance
- Network, system, or data-flow diagrams appropriate to the service
Privacy and data-governance evidence
- Data-processing inventory for the service
- Categories of personal and confidential data
- Hosting and processing locations
- Data retention and deletion approach
- Subprocessor list
- Cross-border data-transfer position
- Data subject request and breach-handling processes
Operational-resilience evidence
- Business continuity plan
- Disaster recovery plan
- Recovery time and recovery point objectives
- Latest continuity or recovery test results
- Backup, restoration, redundancy, and availability approach
- Exit, portability, and service-termination arrangements
Compliance and fourth-party evidence
- Code of conduct and relevant compliance policies
- Sanctions, anti-bribery, or financial-crime controls where relevant to the service
- Use of subcontractors and critical technology providers
- Process for assessing and monitoring those providers
- Regulatory licences or registrations where applicable
A certificate or policy rarely answers every question by itself. The bank still needs to understand whether that evidence applies to the legal entity, product, environment, geography, and service it intends to use. Vendors should map every document to its scope, owner, version, approval date, and expiry or next-review date.
The six failure patterns that delay financial-services vendor onboarding
1. Questionnaire work starts from zero every time
A new spreadsheet arrives and is forwarded around the company. Previous answers are copied from email or an old questionnaire without checking whether they are still correct. The immediate task gets completed, but the company learns nothing reusable.
Better approach: maintain approved answer components linked to current supporting evidence. Reuse should accelerate drafting, not bypass review.
2. No one owns the end-to-end approval journey
Sales owns the customer relationship, security owns technical controls, legal owns contract language, and privacy owns data-processing answers. Each team completes its piece, but nobody owns the dependency map or the overall deadline.
Better approach: assign one onboarding lead who can see every requirement, owner, blocker, submission, follow-up request, and approval condition.
3. Answers and documents contradict each other
The security questionnaire gives one retention period, the privacy schedule gives another, and an old policy contains a third. Even small inconsistencies can create follow-up questions because the bank cannot tell which statement is authoritative.
Better approach: track the source and approver for each answer. Flag conflicts before anything is submitted.
4. Evidence is outdated or has the wrong scope
An expired certificate, an old penetration test, or a parent-company policy that does not cover the contracted entity may not satisfy the request.
Better approach: record effective dates, scope, review dates, expiries, and responsible owners for every evidence item.
5. The vendor cannot explain its service boundary
Risk teams cannot assess what they cannot see. Vague descriptions of data access, hosting, integrations, subprocessors, or operational responsibility create more questions and may cause the bank to assume a broader risk exposure.
Better approach: prepare a concise service profile with architecture, data flows, locations, dependencies, and clear shared-responsibility boundaries.
6. Approval is treated as a one-time event
Banks may reassess vendors periodically or after material changes. New subprocessors, security incidents, major product changes, certificate expiries, and contract renewals can all create new evidence requests.
Better approach: convert the completed onboarding into a living record with reminders, review triggers, and a complete history of what was provided.
A practical vendor-side workflow for faster bank approval
The goal is not to promise an unrealistically fast approval. The bank controls its own review. The vendor's goal is to remove avoidable delay, respond consistently, and make the evidence easy to evaluate.
Step 1: Create a standard service profile
Document the facts that determine onboarding scope:
- Contracting legal entity
- Product or service being delivered
- Intended use by the bank
- Data types processed
- Data and hosting locations
- Production access and integration method
- Subprocessors and critical dependencies
- Availability and recovery commitments
- Bank-side and vendor-side responsibilities
Use this profile to prevent different teams from describing the service differently.
Step 2: Build a governed evidence library
Store each document with an owner, version, scope, approval date, confidentiality level, and next-review or expiry date. Separate customer-shareable evidence from restricted material that requires an NDA or controlled review.
Step 3: Turn the questionnaire into requirements
Do not manage a 300-row questionnaire as one task. Break it into individual requirements and classify each one:
- Answer available and evidence available
- Answer available but evidence missing
- Evidence available but interpretation required
- New fact or decision needed
- Not applicable, with rationale
- Contractual or risk exception requiring approval
Then assign an owner and due date. This makes the real blockers visible.
Step 4: Draft from approved sources
Reuse current answers where the question and service scope genuinely match. Link every material claim to an internal source or evidence item so the reviewer can validate it. Do not allow old questionnaires to become an ungoverned shadow knowledge base.
Step 5: Review for consistency and disclosure
Before submission, compare responses across security, privacy, legal, product, and resilience domains. Confirm that restricted reports are shared through an approved channel and that the response does not reveal secrets, credentials, exploitable technical detail, or unrelated customer information.
Step 6: Manage follow-ups as part of the same case
Keep questions, answers, attachments, decisions, exceptions, owners, dates, and customer feedback together. A follow-up should extend the record rather than start another email chain.
Step 7: Convert approval into ongoing readiness
After activation, schedule evidence refreshes and recurring reviews. Track certificate expiration, policy review, penetration testing, recovery testing, insurance renewal, subprocessor changes, incidents, product changes, and contract renewal.
Where AI helps in vendor onboarding - and where it should not decide
AI can remove coordination work when it operates on controlled company information and keeps people accountable.
Useful applications include:
- Classifying bank requirements by security, privacy, legal, compliance, product, or resilience domain
- Suggesting the right internal owner for each requirement
- Finding potentially relevant approved answers and evidence
- Identifying missing documents, expired evidence, and inconsistent statements
- Drafting a response that cites its source material
- Summarising follow-up requests and highlighting changed requirements
- Tracking gaps, deadlines, renewal dates, and recurring reviews
But AI should not invent a control, guess whether a requirement is satisfied, approve a risk exception, or submit an answer without an accountable human review. A fluent but unsupported response can accelerate the wrong outcome.
The safe pattern is source-linked assistance with human approval:
- Retrieve from controlled, current evidence.
- Show the source used for the draft.
- Highlight ambiguity, missing information, and conflicts.
- Route the response to the accountable owner.
- Record who approved what was sent.
That turns AI into a coordination and preparation layer rather than an unsupervised decision-maker.
How to measure whether vendor onboarding is improving
Track operational measures that connect the post-signature process to customer activation:
- Time from contract signature to first complete submission
- Time from signature to risk approval
- Time from approval to production activation
- Percentage of questions answered from approved, current sources
- Number of unanswered requirements at each review stage
- Number of bank follow-up rounds
- Responses returned for correction because of inconsistency
- Evidence items approaching expiry
- Open remediation items and overdue owners
- Time spent by sales, security, legal, compliance, and product per onboarding
The purpose is not to pressure control teams into accepting risk. It is to separate necessary review time from avoidable waiting, rework, and internal coordination.
Bank vendor onboarding checklist for vendors
Before the contract is signed:
- Confirm the exact service, data, integration, and hosting scope
- Identify the likely risk tier and review domains with the bank sponsor
- Assign one vendor-side onboarding lead
- Identify long-lead evidence and restricted reports
- Surface material gaps or planned remediation honestly
Before submitting due diligence:
- Split the questionnaire into owned requirements
- Verify that every answer matches the contracted service and entity
- Link material answers to current supporting evidence
- Check policy, certificate, insurance, and report dates
- Reconcile security, privacy, legal, compliance, and product answers
- Document why any requirement is not applicable
- Obtain human approval from the accountable owner
Before activation:
- Confirm all approval conditions and remediation commitments
- Record implementation dependencies and responsible owners
- Store the final submitted answers and evidence together
- Capture review, renewal, and evidence-expiry dates
- Define how material changes and incidents will be communicated
Frequently asked questions
How long does bank vendor onboarding take?
There is no universal timeline. It depends on the service's risk, data access, operational criticality, integration complexity, jurisdictions, the bank's governance process, and how complete the vendor's evidence is. Vendors cannot control the bank's review speed, but they can reduce delays caused by missing, stale, contradictory, or unowned information.
What is a TPRM questionnaire?
A third-party risk management questionnaire is a structured set of questions used to assess a supplier's controls and risk exposure. It may cover information security, privacy, business continuity, financial stability, compliance, subcontractors, incident management, data location, and exit planning. Banks often tailor the depth of the questionnaire to the service's risk.
Is a SOC 2 report or ISO 27001 certificate enough for bank vendor due diligence?
Usually not by itself. Independent assurance can answer important control questions, but the bank may still need to confirm scope, exceptions, service-specific architecture, privacy arrangements, resilience, subcontractors, contractual rights, and remediation. Vendors should use certifications as evidence within the response, not as a substitute for answering the bank's actual question.
What is the difference between vendor onboarding and third-party risk management?
Vendor onboarding is the process of approving and setting up a supplier for use. Third-party risk management is broader: it covers how the relationship is planned, assessed, contracted, monitored, changed, and eventually terminated. Onboarding is one important phase in that lifecycle.
Can AI complete bank security questionnaires automatically?
AI can help classify questions, retrieve approved information, suggest drafts, identify evidence, and detect gaps. Fully automatic completion is risky when questions are ambiguous or answers depend on service scope, current controls, legal interpretation, or risk acceptance. Final responses should be source-linked and approved by accountable people.
What causes the most delays after a bank contract is signed?
Common causes include unclear service scope, missing or expired evidence, inconsistent answers, slow internal ownership, unresolved security or privacy gaps, contract exceptions, restricted documents that are difficult to share, and follow-up requests managed across separate email threads.
From signed contract to active customer
We are building an AI-powered onboarding workspace for vendors selling to regulated financial institutions.
It helps vendors:
- Turn bank requirements into clear actions
- Identify missing information before it causes delays
- Provide information through integrations or direct uploads
- Track gaps, deadlines and upcoming requirements
- Coordinate responses across internal teams
- Prepare for ongoing reviews after activation
Winning the deal should not be the start of another unmanaged process.
The next competitive advantage in financial-services sales will be the ability to move from signed contract to approved and active customer - faster and with less manual coordination.
If your company sells to banks and onboarding slows down revenue after the contract is signed, I would like to learn how you manage the process today.
Authoritative sources and further reading
- US banking agencies: Interagency Guidance on Third-Party Relationships - Risk Management
- European Banking Authority: Guidelines on third-party risk management and outsourcing arrangements
- EUR-Lex: Digital Operational Resilience Act (Regulation (EU) 2022/2554)
#Banking #VendorOnboarding #ThirdPartyRiskManagement #B2BSaaS #AIautomation